Meta Built Face Recognition for Smart Glasses: No Law Protects Bystanders
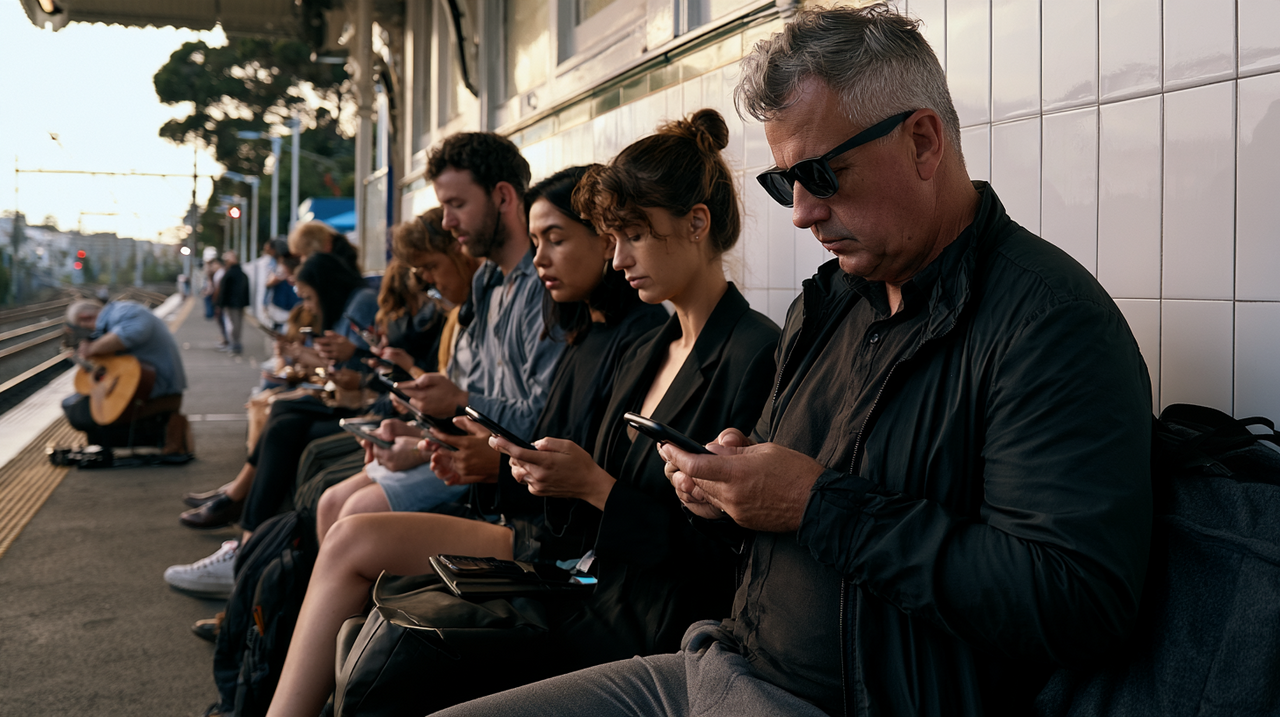
Picture an ordinary Tuesday on an ordinary platform. A train is late, commuters thumb their phones, a busker tunes a guitar against a tiled wall. Somewhere in that crowd a man in sunglasses glances your way for slightly longer than feels polite, and then looks away. You think nothing of it, because there is nothing to think. You have not been photographed in any sense you would recognise. No flash, no shutter, no phone raised to frame your face. And yet, in the half-second of that glance, a camera tucked into the hinge of his glasses has captured your face, a model running on the companion app on his phone has reduced the geometry of your features to a string of numbers, and that string has been compared against a store of other such strings held on the device. If you were a match, your name would have surfaced in his field of view. If you were not, the system would simply have filed the measurement away and moved on to the next face in the crowd. You would never know either way. That is the entire point.
This is not a thought experiment. In June 2026, WIRED reported that Meta had quietly embedded a face-recognition system called NameTag into the companion app that pairs with its Ray-Ban and Oakley smart glasses, an app that has by now been installed on more than fifty million phones. According to the reporting, the system was dormant but complete: capable of identifying any person captured by the glasses' camera, converting a face into a unique biometric signature, and matching it against profiles stored locally, all without any notification to the person being identified. Andy Stone, Meta's vice-president of communications, told WIRED that the feature was “purely exploratory” and that the company had reached “no final decision” about it — this of a system whose components had been shipped across a series of routine app updates beginning in January. On 5 June, a day after publication, after an outcry led by the Electronic Frontier Foundation, the company stripped the code from the app, and the EFF declared a partial victory. The relief was real. It was also beside the point. Because removal answers a narrow question — is the feature live right now? — while leaving the larger one exactly where it was: when a company can build ambient surveillance of strangers into a mass-market consumer object and distribute it to millions of people before anyone outside the building knows it exists, what does an ordinary person walking down the street actually have to protect them?
The Shape of the Thing That Was Built
Begin with the mechanism, because the mechanism is the argument in miniature. On the reporting, NameTag ran three AI models in sequence. The first swept each frame for faces. The second cropped and aligned whatever it found. The third converted that cropped face into a faceprint — a vector of 2,048 numbers describing the geometry of one particular human head — and compared it against a store of faceprints held on the device. The string of numbers is not a figure of speech. It is the literal artefact: a person reduced to two thousand and forty-eight measurements in the time it takes a stranger to look up and look away. And the system did not confine itself to the faces it already knew. A face it could not match was cropped, indexed and stored locally regardless, kept for future processing, which means the machine was not merely answering the question of whether it recognised someone. It was accumulating strangers against the day it might.
It helps to be precise about what NameTag is and is not, because the precision is where the alarm lives. This is not a data breach, the familiar modern catastrophe in which a company that meant to keep your information safe fails to, and your records spill out through a hole someone forgot to close. It is not a hack, in which an outside party defeats a system designed to keep them out. A breach and a hack are failures of intention; somebody wanted to protect you and could not. NameTag is the opposite. It is a capability that works precisely as designed, and the design is to identify people who have not asked to be identified, who do not know they are being identified, and who have no means of objecting because they are unaware there is anything to object to. The harm is not the malfunction. The harm is the function.
Nor is it surveillance in the sense we have spent two decades learning to dread. The mental model most of us carry is of a watcher with a motive: a government tracking dissidents, a corporation harvesting behaviour to sell us things, a platform building a profile to keep us scrolling. Those are concentrated powers, and concentrated power can at least in principle be named, regulated, sued, voted against. What the glasses describe is something stranger and more diffuse. The watcher is not a state or a firm. The watcher is whoever happens to be standing near you wearing a particular pair of sunglasses — a stranger on a train, a man at the next table, someone who passed you on the escalator and whom you will never see again. The infrastructure of identification has been miniaturised, commodified, and handed out at retail. Surveillance has been democratised in the bleakest possible meaning of the word: not made accountable to the many, but made available to anyone.
That diffusion is the genuinely new thing. We have had powerful face-recognition systems for years, and we have had reasons to fear them. But those systems lived in places — in police control rooms, in airport queues, in the data centres of a company called Clearview AI that scraped the open web for faces and sold the results to law enforcement. They were terrible, but they were located. You could at least say where the danger was. NameTag proposes to dissolve that location entirely, to take the faceprint and seed it into the ambient environment, into the everyday optics of people who are simply going about their day with a camera on their face and a model in their pocket. The question stops being “is the government watching me” and becomes “is anyone, and how would I ever know.” There is no control room to point at. There is only the crowd.
How the Glasses Got On Your Face
None of this fell from the sky. The smart glasses at the centre of the story are the product of a partnership between Meta and EssilorLuxottica, the Italian-French eyewear conglomerate that owns Ray-Ban and Oakley among a great many other brands and dominates the global market for spectacles. The collaboration began with the underwhelming Ray-Ban Stories in 2021 and matured, in October 2023, into the Ray-Ban Meta line, which paired a discreet camera, open-ear speakers, and an on-board AI assistant into a frame almost indistinguishable from ordinary sunglasses. The Oakley Meta range followed, aimed at athletes and the outdoors. And then the things began to sell. EssilorLuxottica reported that around two million units had moved between launch and early 2025, and that sales more than tripled across 2025 alone, with something on the order of seven million glasses sold in that year and roughly nine million in total since the line began. Revenue from the AI glasses then nearly doubled again year on year across the first half of 2026. A new model, the Ray-Ban Display, arrived at $799 with a screen set into one lens, operated by hand gestures and a neural wristband that reads the electrical signals in the wearer's forearm; its international launch, promised for early 2026, was pushed back because demand in the United States was, in Meta's word, “unprecedented”. The two companies now speak of production capacity running to twenty million units or more by the end of 2026, and of exceeding thirty million if the demand holds.
The hardware numbers matter, but the number that should command attention is a different one. The companion app — the software that pairs with the glasses, manages their settings, and, crucially, runs the AI that interprets what the camera sees — has been installed more than fifty million times. That gap between glasses sold and apps installed tells its own story about the way these systems propagate: the camera is the visible artefact, the thing you might notice on someone's face, but the intelligence lives in software that can be updated silently and at scale, pushed to tens of millions of devices in the ordinary churn of a Tuesday-morning patch. A feature does not need to be announced to arrive. It does not need a launch event, a keynote, a press release. It can simply appear, fully formed and waiting, inside an update labelled “bug fixes and performance improvements.” That is, on the reporting, more or less how NameTag arrived: not in one dramatic release but in pieces, distributed across several updates from January onward, each component innocuous on its own, the whole only legible once someone troubled to assemble it.
The design language of the glasses compounds the problem. The entire commercial proposition is that they look normal. Ray-Ban and Oakley are not obscure gadget brands; they are the default eyewear of beaches and high streets, and the smart versions are deliberately hard to tell apart from the dumb ones. There is a small capture light meant to indicate when recording is under way, a concession wrung from earlier privacy criticism, but it is easy to miss in daylight, easy to obscure, and in any case indicates recording rather than identification. A bystander who happened to notice the light would learn that a video was being taken, not that their face was being measured and matched. The very features that make the glasses a successful consumer product — their ordinariness, their ubiquity, their disappearance into the visual furniture of everyday life — are precisely the features that make them an effective instrument of covert identification. You cannot opt out of a surveillance device you cannot distinguish from a pair of sunglasses.
The Two Consents, and Why Only One Exists
There is a serious argument for the convenience of all this, and it deserves to be put at its strongest rather than waved away. A person who is bad with names meets a colleague at a conference and is spared the small humiliation of forgetting. A man with early dementia walks into a family gathering and the glasses gently remind him who his grandchildren are. A blind user, who cannot read a face at all, is told that the person approaching is a friend. These are not trivial goods. The promise of ambient computing has always been that the machine recedes into the background and quietly smooths the friction of ordinary life, and recognition is, on its face, exactly that kind of smoothing. Meta and its defenders can point, with some justice, to genuine accessibility cases and to the simple human pleasure of not being the person who blanks on a name. If the technology only ever did those things, for people who wanted it, the objection would be hard to sustain.
But the argument contains a fatal slippage, and the slippage is the word “consent.” There are two consents at stake here, and only one of them can ever be given. The wearer consents. He buys the glasses, installs the app, agrees to the terms, and decides to switch the feature on. Whatever happens to him — the data he generates, the analytics he feeds, the profile he builds of himself — he has, in some meaningful if imperfect sense, signed up for. The accessibility cases all live on this side of the line. The blind user, the man with dementia, the bad-with-names colleague: each of them is consenting to a tool that operates on their own experience. That is consent the wearer can give, and it is real.
The bystander cannot give it. This is the structural fact the convenience argument cannot survive, and it is worth stating plainly because so much of the public conversation slides past it. When the man in sunglasses identifies you on the platform, you are not a user of the system. You are its raw material. You did not buy the glasses, did not install the app, did not read the terms, did not toggle anything on or off. You were merely present, in public, with a face, and that was sufficient. There is no screen on which you might have tapped “I agree,” because the entire transaction is built to require nothing of you and to tell you nothing. Every framework we have for managing the privacy harms of the last twenty years — terms of service, cookie banners, privacy settings, the whole apparatus of notice-and-consent — assumes a relationship between a person and a service that person has chosen to use. The bystander has no such relationship. The bystander has been conscripted into a system to which they are not a party, and from which there is, by design, no exit. You cannot withdraw a consent you were never asked to give.
A Company That Has Paid This Bill Before
If there is a reason to doubt that good intentions will hold the line, it is that Meta has stood exactly here before, and the standing was expensive. In 2008, Illinois passed the Biometric Information Privacy Act, known universally as BIPA, the strictest law of its kind in the United States. Its core demands are simple and onerous: a company that collects a person's biometric identifiers — a faceprint, a fingerprint, a voiceprint — must obtain that person's informed written consent first, must publish a retention and destruction schedule, and must not profit from the data. What gives BIPA its teeth is a feature most American privacy laws conspicuously lack: a private right of action with statutory damages. An ordinary Illinoisan does not have to wait for a regulator to act, or prove they suffered measurable financial loss. They can sue on their own behalf, and the statute, rather than the plaintiff's bank statement, sets the sum: a thousand dollars for a negligent violation, five thousand for a reckless or intentional one. That structural choice — a wrong made actionable by the person wronged, at a price the legislature fixes in advance — is the reason BIPA matters far beyond Illinois.
It matters somewhat less than it did, and the reason is instructive. For years the open question under the Act was whether that sum attached to every scan or only to the first, and in 2023 the Illinois Supreme Court answered it in Cothron v. White Castle System: a claim accrued each time a biometric identifier was collected. The multiplier was the whole of the deterrent. A company that fingerprinted the same worker twice a day for five years faced a figure with a great many zeros in it, which is precisely why the figure concentrated minds. Within eighteen months the legislature had taken it away. Senate Bill 2979, signed by Governor J. B. Pritzker and effective from 2 August 2024, provides that repeated collection of the same identifier from the same person by the same method amounts to a single violation, recoverable once — the first amendment to BIPA in sixteen years, and an amendment in one direction only. In April 2026 the Seventh Circuit held, in Clay v. Union Pacific Railroad, that the change was remedial rather than substantive and therefore applied backwards, to every case already pending when it passed. The private right of action survives, and it remains the most effective biometric-privacy mechanism in American law. But the part of it that made a large company stop and calculate has been filed down, and filed down retrospectively, by the same legislature that sharpened it. That is worth holding on to, because it describes a gravitational pull the rest of this story obeys: remedies that genuinely deter do not stay sharp on their own.
Facebook learned what it costs. The company's old Tag Suggestions feature, switched on by default from 2011, scanned every uploaded photo and built faceprints of the people in them without the written consent BIPA required. The resulting class action, In re Facebook Biometric Information Privacy Litigation, settled for $650 million, approved by Judge James Donato of the Northern District of California in early 2021 — at the time the largest all-cash privacy settlement in history, covering roughly 1.6 million Illinois users. Then Texas, which has its own biometric statute, the Capture or Use of Biometric Identifier Act, or CUBI, dating to 2009, brought the first enforcement action ever filed under it. In July 2024, Attorney General Ken Paxton announced that Meta would pay $1.4 billion to resolve allegations that it had captured the facial geometry of Texans, again through Tag Suggestions, without consent — the largest settlement ever obtained by a single state from a single company. Two billion dollars, in round terms, for the same underlying behaviour: collecting faceprints from people who never agreed to it.
And yet the deepest lesson of those settlements may be the wrong one to take comfort in. The EFF, in its commentary on the Texas case, made an observation that should haunt anyone inclined to treat the figures as deterrence: the violation went on for years, and would have been stopped far sooner had ordinary Texans been able to sue the way Illinoisans can. The settlements, enormous as they are, arrived after the harm was complete, as a cost levied at the end rather than a barrier raised at the start. For a company of Meta's scale, a billion-dollar payout some years after the fact is not a wall. It is a line item — a calculable, plannable expense to be weighed against the value of the data and the advantage of moving first. When penalties function as the price of a strategy rather than a prohibition on it, they cease to deter and start to license. The history does not reassure. It tells us that Meta has done this before, knew exactly what it was doing when it did, and paid the bill as a cost of doing business. NameTag is not a departure from that pattern. It is its continuation, in a more intimate medium.
Nor has the pattern closed. On 4 September 2026, lawyers at Wexler Boley & Elgersma filed a proposed class action in the Northern District of Illinois on behalf of Francisco Alvarez, an Illinois resident, and his minor child, of Jeremy Wahl of California and his minor daughter, and of a class they estimate in the millions. The complaint alleges that Meta harvested facial images from Facebook and Instagram without notice and used them to train and test NameTag, to generate the faceprints it would match against, and to build image-generation models including Emu and Muse Image. The counts are brought under BIPA's requirement to publish a retention and destruction schedule and its requirement of informed written consent before collection, alongside claims under California privacy law. Meta says the suit is “without merit and misrepresents our work”, that it has been transparent about using information to develop AI products, that it is not building a universal database of faces, and that NameTag was never released to consumers. The allegation that should arrest anyone reading it, though, is not about users at all. The images are said to have come from users and non-users alike — from people who never opened an account, never clicked through any terms, never entered into any relationship with the company, and whose faces happened to appear in somebody else's photograph. That is the second consent, the one that cannot be given, going missing a second time and much earlier: the bystander conscripted not at the moment of identification but years before it, to supply the raw material for the system that will one day decline to ask them. And the claim arrives in Illinois, under the one statute that lets an ordinary person bring it, in the jurisdiction whose remedy for bringing it has just been cut to a single recovery.
What the Harvard Students Already Showed
It would be a mistake to imagine that any of this required Meta's blessing, and the clearest proof came not from a corporation but from two undergraduates. In the autumn of 2024, the Harvard students Caine Ardayfio and AnhPhu Nguyen built a system they called I-XRAY using nothing more than a commercially available pair of Ray-Ban Meta glasses and software they wrote themselves. The glasses streamed video; their program scanned that stream for faces, ran them through a public face-search engine, and then chained the results to other public databases to pull up names, addresses, occupations, relatives, and in some cases fragments of social security numbers — all in something close to real time. In their demonstration they identified strangers on public transit and produced, within seconds, a dossier the stranger had no idea was being assembled.
The students were explicit that the point was not the glasses in particular. As Nguyen put it, the same thing could have been done with a phone camera; the project was a demonstration of what was already possible, built to raise alarm rather than to provide a tool. And that is exactly why it matters to the NameTag story. It establishes that the capability has been sitting in the open, reachable by two motivated undergraduates with off-the-shelf hardware, for years. The hard part was never the optics or the on-device cleverness. The hard part — the part that requires the scale, the distribution, the fifty million installed apps, and the willingness to absorb the legal consequences — is putting that capability into the hands of millions of ordinary people as a default, frictionless, supported feature of a product they already own. That is the line a company crosses that a pair of students cannot. I-XRAY proved the technology was loose. NameTag proposed to make it ambient.
The same lineage runs through Clearview AI, the firm that scraped something on the order of tens of billions of images from the open internet — Facebook, LinkedIn, anywhere a face could be found — to build a search engine for faces that it sold to police departments and others. Clearview has been fined repeatedly under European data-protection law, including a €30.5 million penalty from the Dutch regulator, and in the United States it settled with the American Civil Liberties Union under BIPA in 2022, agreeing to a nationwide injunction limiting which private entities could use its database. Clearview showed that the back end — the vast index of faces against which any new face can be matched — already exists and can be built from public material. The glasses supply the missing front end: the eyes, distributed across millions of faces in the street. Put the two halves together, on-device or in the cloud, and you have a complete machine for identifying strangers, assembled from parts that are each, individually, already real and already deployed.
The Patchwork and the Hole at Its Centre
Confronted with all this, an American walking down the street might reasonably ask what law protects them. The honest answer is: it depends entirely on which street, and mostly the answer is none. The United States has no federal baseline privacy law, no national statute that says, simply, that your biometric identity belongs to you and may not be taken without your agreement. What exists instead is a patchwork, and the patches are thin. Illinois has BIPA, with its private right of action, and that is why the largest reckonings have happened there. Texas has CUBI, enforceable only by its attorney general, which is why its billion-dollar settlement required the state to act on its citizens' behalf. Washington has a biometric statute; a handful of comprehensive state privacy laws passed since 2023 gesture at biometric data as a sensitive category. But the overwhelming majority of Americans live in states where no specific biometric law applies to them at all, where a stranger identifying them in public breaks no statute they could name.
There is motion, of a kind. At least ten state legislatures took up bills mentioning smart glasses during 2026, though most were aimed at keeping the devices out of schools. Two reached further: Louisiana's House Bill 410, which would oblige anyone recording an in-person conversation to say so or face a suit for damages, and California's Senate Bill 1130, which would make it a crime to record a person with a wearable device in a place of business where privacy is reasonably expected, and would bar the sale of wearables lacking a clear recording indicator. At federal level, Representative Zoe Lofgren has reintroduced the Online Privacy Act, a comprehensive bill running to individual rights, corporate duties, security, breach notification, enforcement and a standalone Digital Privacy Agency to administer the lot. Senators have written letters, to Meta in March and to the executive branch in May. None of this is yet a law that protects the man on the platform. A bill introduced is not a bill passed, three previous versions of the Online Privacy Act were introduced and none of them advanced, and a statute that keeps glasses out of classrooms does nothing whatever for the stranger standing behind you in a queue. The patchwork is being stitched at its edges while the hole in the middle stays precisely the size it was.
Which is why the most revealing response of the year came not from a legislature but from institutions that had stopped waiting for one. In July 2026 the New York State Unified Court System barred eyewear and headwear containing a camera, microphone or recording technology from more than twelve hundred court facilities. In August, His Majesty's Courts and Tribunals Service extended an equivalent prohibition across every criminal, civil and family court in England and Wales, instructing security staff to confiscate the devices on entry and return them on exit. The service explained itself briefly: “There are clear restrictions on taking images or videos within courts and tribunals which is why the use of Meta glasses is prohibited.” Notice what the courts did not do. Smartphones remain admitted, on the condition that they are not used to record — a rule about conduct, enforceable because the conduct can be seen. No such rule could be written for the glasses, because the glasses record while merely being worn, and the whole of their design is devoted to making that state indistinguishable from the other one. A conduct-based rule requires an observable act, and here there is none. So the only instrument left was physical exclusion: confiscation at the threshold, the last resort of an institution with no law to invoke. That is what a legal vacuum looks like in practice, and it is worth noticing who gets to use it. A court can take the glasses off a man at its door. A woman on a railway platform cannot.
The contrast with Europe is instructive, and not entirely reassuring in the direction one might expect. Under the General Data Protection Regulation, biometric data processed for the purpose of uniquely identifying a person is “special category” data under Article 9, subject to a default prohibition that can be lifted only by narrow conditions, chief among them explicit consent — the very consent the bystander cannot give. The penalties run to the higher of €20 million or four per cent of global annual turnover, which for a company of Meta's size is a figure with real heft. The EU AI Act goes further still, and its architecture is the one that most directly answers the NameTag problem: it treats remote biometric identification as a category of special danger, banning the real-time variety in publicly accessible spaces for law enforcement save for tightly drawn exceptions, and placing heavy constraints on the rest. Those prohibitions have been in force since February 2025. Europe, in other words, has at least begun to legislate against the specific shape of the harm: the identification of people, at a distance, in public, without their knowledge.
Yet even Europe's framework was built with the wrong threat model in mind. The AI Act's most stringent rules contemplate the state as the principal actor — the police force running real-time recognition over a crowd, the public authority building a watch-list. That is a reasonable historical fear, but it is not quite the NameTag fear. NameTag is not the state. It is a private individual, a consumer, a man in sunglasses, operating a device he bought at retail, processing the faces of strangers for his own private ends. The law's careful exceptions for law enforcement, its calibration around public authorities, do not map cleanly onto a world in which the surveillant is your fellow passenger. The frameworks we have, even the good ones, are aimed slightly to one side of where the danger has actually moved. They were built to constrain the watcher in the control room. The watcher has left the control room and is now standing next to you on the platform.
The state, meanwhile, has not obligingly stayed behind in the control room while the danger moved on. In its budget request for the 2027 fiscal year, the Department of Homeland Security proposed developing smart glasses for its immigration officers — eyewear that would allow an officer to photograph a person in the street, covertly, and run the image through biometric identification without breaking stride. In May 2026, Senators Markey, Merkley and Padilla led colleagues in demanding that the department abandon the proposal. What this shows is not that the point about threat models was wrong but that it was understated. The two models are not succeeding one another, the private watcher quietly replacing the public one. They are converging on the same hardware. The state is reaching for the identical miniaturised consumer form factor, which means the rules built for the control room — rules that presume a system, a premises, a procurement, an identifiable deployment capable of being authorised and audited — do not cleanly bind the state either, once its officers are simply people in the street wearing sunglasses. The device collapses the distinction on which the law was built. Whatever else a pair of glasses on a face may be, it is not a control room, and a framework that regulates control rooms will keep missing, whoever happens to be wearing them.
What Proportionate Would Actually Mean
So what would a response proportionate to the scale of the thing being built actually require? Begin by naming what it cannot be, because the NameTag episode has already shown us the shape of the inadequate answer. It cannot be the after-the-fact settlement, the billion dollars paid years later once the data is collected and the precedent is set. We have run that experiment twice, at $650 million and $1.4 billion, and the only lesson Meta appears to have drawn is how to price it. A penalty that arrives after the capability has been built, shipped, and switched on is not a constraint on the behaviour; it is a tax on it, and a company with sufficient revenue treats a tax as a permission slip. Proportionality has to mean intervention before deployment, not compensation after.
That points toward a cluster of measures, each of which trades cleanly against a specific failure the episode exposed. The first is ex-ante product gating: a requirement that a consumer device capable of biometric identification of non-consenting third parties cannot be brought to market, or have such a capability shipped to it, without prior regulatory clearance — the way a new aircraft or a new drug must be cleared before it flies or is sold, rather than recalled after it crashes. The dormant-code manoeuvre, in which the components arrive piecemeal in routine updates and lie waiting to be activated, is precisely the move that ex-ante gating exists to forbid. The second, and bluntest, is a flat prohibition on covert biometric identification of strangers in consumer devices — a line that says some capabilities are not products at all, that the identification of non-consenting bystanders is simply not a feature a sunglasses company may ship, regardless of clearance, regardless of consent flows the wearer might click through. Many democracies already accept that certain instruments cannot be sold to the public no matter the demand for them. The case that ambient face-recognition of strangers belongs in that category is not exotic.
The third measure addresses the consent asymmetry directly: statutory bystander rights, a recognition in law that the person identified — not merely the person doing the identifying — has standing and an interest, and that processing their faceprint without their agreement is a wrong done to them specifically. And the fourth is the mechanism that makes the rest enforceable rather than aspirational: a private right of action with statutory damages, on the BIPA model. This is the single most important lesson the whole history teaches. The reason Illinois has produced the largest reckonings is not that Illinoisans are more private by temperament; it is that they can sue, individually, without proving financial loss, for a sum the legislature has fixed in advance. That structure converts a diffuse, hard-to-quantify harm — the silent taking of your face — into a concrete liability a company must price in before it acts rather than after it is caught. Illinois has since trimmed that mechanism, capping recovery at one violation per person however many times the face was scanned, and the Seventh Circuit has applied the cap backwards to suits already filed. It would be easy to read the narrowing as a reason to abandon the model. It is better read as instruction in how the model must be built. The structural achievement is the standing, not the multiplier: an ordinary person, with no lawyer on retainer and no financial loss to document, who can nonetheless make a company answer for what was done to their face. Nothing else in American privacy law gives them that. But the Illinois experience shows what happens once the numbers grow large enough to be felt: the remedy that bites comes under sustained and well-funded pressure to stop biting, and it was amended within eighteen months of acquiring real force, in a form that reached backwards into cases already under way. A federal right of action worth having would have to be drafted in the expectation of that pressure rather than in innocence of it, with damages scaled to the scope of a collection rather than to one moment of it, and a floor beneath which the sum cannot later be filed away. A federal baseline privacy law carrying that mechanism would do more to deter the next NameTag than any number of nine-figure settlements arriving years too late. The EFF, in declaring its partial victory, said as much: removal is not a change of heart, and good will is not a regulatory regime.
Why Removal Is Not an Answer
It is worth steelmanning the reassurance one more time, because it is sincere and it is not nothing. Meta stripped the code. The feature is not live. A company watched the public react, listened, and pulled back; the system worked, in the sense that exposure produced retreat. Those who take comfort in this are not foolish. The press did its job, civil society did its job, and a powerful firm changed course in days rather than years. If you believe in the corrective power of sunlight, the NameTag episode is a small vindication of it.
And yet the structure of the relief is exactly what should disturb us. Notice the sequence. The capability was conceived, built, and distributed to fifty million devices before anyone outside Meta knew it existed. The public's only opportunity to object arrived after the system was already sitting, complete, in tens of millions of pockets — and arrived not because Meta disclosed anything but because a journalist found it. The removal we are asked to celebrate was an act of grace, granted by the company that built the thing, on a timetable the company controlled, in response to an exposure the company did not choose. Nothing in that sequence is a right held by the bystander. At every step, the person whose face was at stake was a spectator to a negotiation between Meta and its critics, with no seat at the table and no lever to pull. The code can be re-added as quietly as it was removed; Meta has pointedly declined to say it will not return. A protection that exists only at the discretion of the entity it is meant to protect you from is not a protection. It is a reprieve.
And there is no longer much need to speculate about whether it will return. Two months after the code came out of the app, the intention surfaced in the patent record. United States patent application 2026/0238876 A1, “Smart Cameras Enabled by Assistant Systems”, was filed on 4 February 2026 and published on 13 August, the latest continuation in a chain of filings reaching back to 2019. It describes an assistant that combines the glasses' cameras with facial recognition, expression analysis, gaze tracking and object recognition: software that identifies the people in the wearer's line of sight, generates video clips automatically according to who is present, reads faces and gestures through what the document calls semantic scene understanding, and — this is the part to sit with — ranks the people around the wearer by how interesting they are, drawing on stored data about the wearer's social relationships to perform the sorting. The crowd on the platform, scored and ordered. Meta was prosecuting that application through the same months in which it was describing NameTag to WIRED as purely exploratory, a matter on which no final decision had been reached. Both things can be true in the narrow sense that an application is not a product and a patent is not a shipping date. But companies do not spend years and lawyers pursuing claims over a direction they have abandoned. Stripping the code retired a feature. It did not retire the capability, and the capability is now a matter of public record, in the company's own filing.
This is the deepest reason removal does not answer the structural question. The question was never “is NameTag running today.” The question is whether an ordinary person has any standing, any right, any enforceable claim over what is done with their face by a stranger in the street — and the answer that the episode actually delivers is no. What stopped NameTag was not a law the bystander could invoke but a public-relations calculation the bystander could only hope would break their way. Change the calculation — a quieter rollout, a more distracted news cycle, a feature framed as accessibility rather than identification, a competitor shipping first — and the same capability lands and stays. The thing that saved the strangers on the platform this time was luck wearing the costume of accountability.
The Face You Cannot Take Off
There is a reason faces occupy a special place in the law and in our intuitions, and it is worth ending there. You can change a password that leaks. You can cancel a card, freeze an account, move house, choose a new phone number. The whole machinery of modern data protection rests, quietly, on the assumption that identifiers are in some sense revocable — that if the link between you and a piece of information is compromised, the link can be broken and remade. Your face breaks that assumption. It is not a credential you can rotate. It is the one identifier you carry, exposed, into every public space, every single day, with no means of withdrawing it short of a mask. When your faceprint enters a system without your consent, there is no reset. The harm does not expire when the breach is patched. It persists for as long as you have a face, which is to say for the rest of your life.
That permanence is what raises ambient biometric identification of strangers to its own category of harm — distinct from the breach, distinct from the hack, distinct even from the older surveillance we learned to fear. It is not the loss of something you can replace. It is the quiet appropriation of something you cannot. And it is inflicted not by an adversary you could name and confront but by the ordinary ambient condition of being in public near someone wearing a camera and carrying a model. The man in sunglasses on the platform may have meant you no harm at all. He may simply have been bad with names. The system does not care about his intentions, and neither, finally, should the law. What matters is that the capability existed, that it was built deliberately and shipped to millions, and that the only thing standing between you and it, on that ordinary Tuesday, was the hope that someone, somewhere, would find the code in time. We can do better than hope. But only if we decide that a face is not a feature, and that the stranger's right to know your name ends precisely where your right not to be known begins.
References and Sources
- Biometric Information Privacy Act, 740 ILCS 14 (Illinois, 2008).
- Senate Bill 2979 (Illinois, 2024), amending 740 ILCS 14/20 to limit an aggrieved person to a single recovery for repeated collection of the same biometric identifier by the same method. Signed by Governor J. B. Pritzker; effective 2 August 2024.
- Cothron v. White Castle System, Inc., Supreme Court of Illinois (February 2023), holding that a BIPA claim accrues on each collection or transmission of a biometric identifier.
- Clay v. Union Pacific Railroad Company, No. 25-2185, United States Court of Appeals for the Seventh Circuit (1 April 2026), holding the 2024 BIPA damages amendment retroactive to pending cases.
- Capture or Use of Biometric Identifier Act, Texas Business and Commerce Code, Chapter 503 (Texas, 2009).
- In re Facebook Biometric Information Privacy Litigation, No. 15-cv-03747, United States District Court for the Northern District of California (final approval, James Donato J., February 2021).
- Office of the Attorney General of Texas (2024) “Attorney General Ken Paxton Secures $1.4 Billion Settlement with Meta Over Its Unauthorized Capture of Personal Biometric Data.” Press release, 30 July 2024.
- Electronic Frontier Foundation (2024) “Texas Wins $1.4 Billion Biometric Settlement Against Meta. It Would Have Happened Sooner With Consumer Enforcement.” Deeplinks blog, July 2024.
- Alvarez et al. v. Meta Platforms, Inc., No. 1:26-cv-10773, United States District Court for the Northern District of Illinois (class action complaint filed 4 September 2026; Wexler Boley & Elgersma LLP).
- WIRED (2026) “Meta's Hidden NameTag: Inside the Face-Recognition System Quietly Shipped to Smart Glasses.” Investigation, June 2026.
- Electronic Frontier Foundation (2026) “VICTORY: Meta Strips Facial Recognition Code From Smart Glasses App After Public Outcry.” Deeplinks blog, June 2026.
- United States Patent Application Publication 2026/0238876 A1, “Smart Cameras Enabled by Assistant Systems.” Meta Platforms, Inc. Filed 4 February 2026; published 13 August 2026.
- Regulation (EU) 2016/679 (General Data Protection Regulation), Article 9, “Processing of special categories of personal data.”
- Regulation (EU) 2024/1689 (Artificial Intelligence Act), Article 5, “Prohibited AI practices” (real-time and post remote biometric identification provisions; in force from 2 February 2025).
- American Civil Liberties Union (2022) “In Big Win, Settlement Ensures Clearview AI Complies With Groundbreaking Illinois Biometric Privacy Law.” Press release, May 2022.
- Autoriteit Persoonsgegevens / Dutch Data Protection Authority (2024) Decision fining Clearview AI €30.5 million for unlawful biometric database.
- Markey, E. J., Wyden, R., and Merkley, J. (2026) Letter to Meta CEO Mark Zuckerberg on facial recognition in smart glasses. Office of U.S. Senator Edward J. Markey, 17 March 2026.
- Markey, E. J., Merkley, J., Padilla, A. et al. (2026) Letter to the Secretary of Homeland Security opposing the development of biometric smart glasses for immigration officers. Office of U.S. Senator Edward J. Markey, May 2026.
- Online Privacy Act of 2026, H.R. 8014, 119th Congress (introduced by Rep. Zoe Lofgren, 19 March 2026).
- Senate Bill 1130 (California, 2026), Wearable Device Privacy Protection Act; and House Bill 410 (Louisiana, 2026), on notice requirements for in-person recording.
- New York State Unified Court System (2026) Memorandum prohibiting smart glasses and other recording eyewear in Unified Court System facilities, effective 20 July 2026.
- HM Courts & Tribunals Service (2026) Prohibition on Meta smart glasses in criminal, civil and family courts in England and Wales, August 2026.
- Ardayfio, C. and Nguyen, A. (2024) “I-XRAY” demonstration of real-time facial identification using Ray-Ban Meta smart glasses. Harvard University student project, documented in contemporaneous reporting, October 2024.
- EssilorLuxottica / CNBC (2026) “Ray-Ban maker EssilorLuxottica says it more than tripled Meta AI glasses sales in 2025.” Reporting on Meta–EssilorLuxottica smart-glasses sales figures, February 2026.
- EssilorLuxottica (2026) First-half 2026 results and accompanying commentary on AI glasses revenue growth, Ray-Ban Display availability and production capacity, July 2026.
Tim Green UK-based Systems Theorist & Independent Technology Writer
Tim explores the intersections of artificial intelligence, decentralised cognition, and posthuman ethics. His work, published at smarterarticles.co.uk, challenges dominant narratives of technological progress while proposing interdisciplinary frameworks for collective intelligence and digital stewardship.
His writing has been featured on Ground News and shared by independent researchers across both academic and technological communities.
ORCID: 0009-0002-0156-9795 Email: tim@smarterarticles.co.uk
Listen to the free weekly SmarterArticles Podcast